
This page is about connecting external agents to OpenOps. For the AI assistant built into OpenOps, see AI Assistance.
Prerequisites
- An OpenOps environment with the MCP server enabled. If you administer the environment, see Enabling the MCP server.
- A user account in that OpenOps environment.
- An AI agent that can connect to remote MCP servers and sign in through your browser, such as Claude Code, Codex, or the Claude app.
<YOUR_OPENOPS_HOST> with the host you use to open OpenOps in your browser.
Connecting your agent
There are two ways to add the OpenOps MCP server to an agent: run the agent’sadd command, or add an entry to its configuration file. Both point the agent at the same URL. After adding the server, authorize it once from the agent, as described in Authorizing access.
Claude Code
Claude Code
Run the following command:Alternatively, add the server to Run 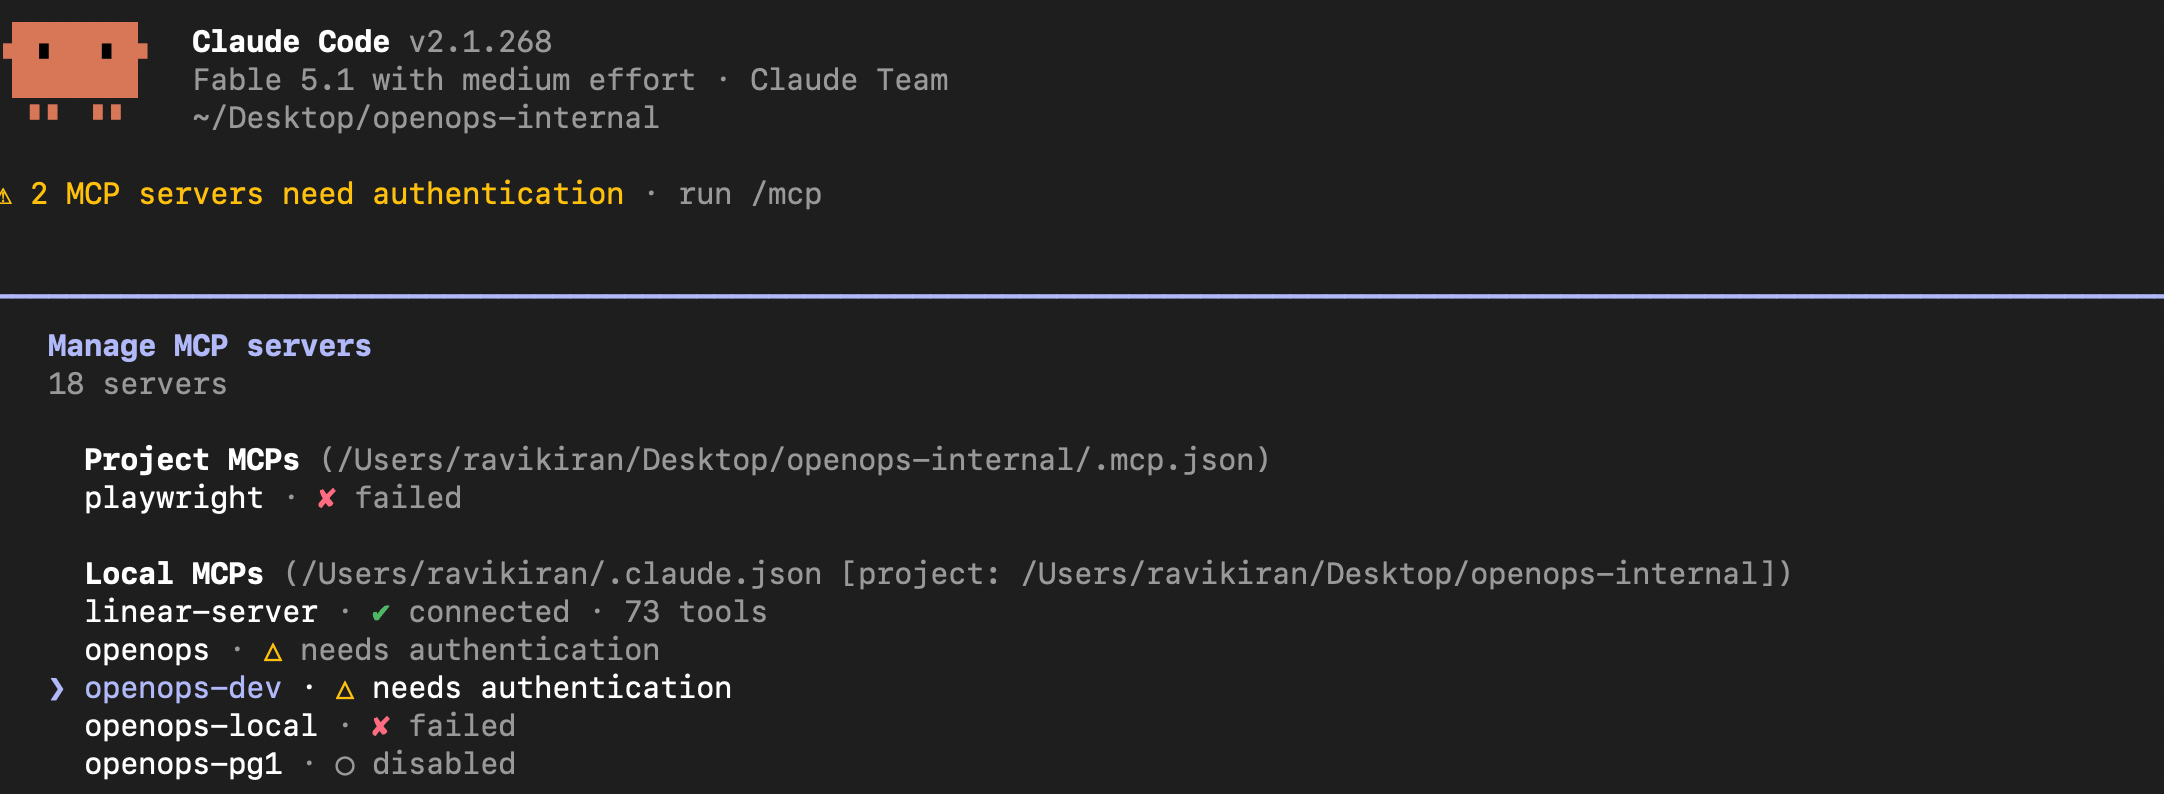
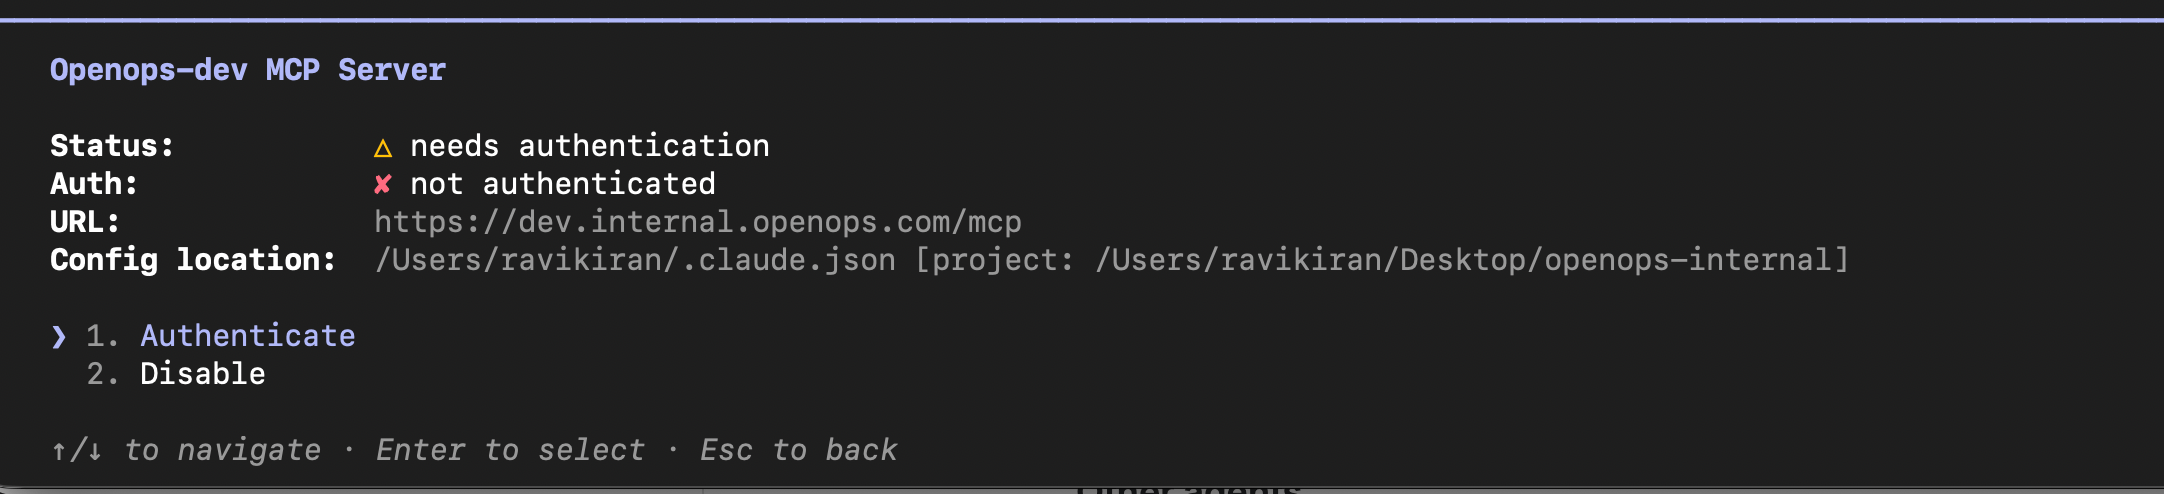
.mcp.json in your project, or to ~/.claude.json for all projects:/mcp inside Claude Code and select openops:claude mcp login openops from your terminal.claude mcp remove openops.Codex
Codex
Run the following commands:Alternatively, add the server to Codex doesn’t start the authorization flow on its own, so the
~/.codex/config.toml and then run codex mcp login openops:login command is required in both cases. The Codex CLI, the Codex IDE extension, and the ChatGPT desktop app share this configuration file.Claude
Claude
In the Claude desktop or web app, go to Settings → Connectors, click Add custom connector, enter the server URL, and click Add. Then click Connect next to the OpenOps connector to authorize. To remove it later, open the connector’s menu and choose Remove.
Other clients
Other clients
Any client that can connect to a remote MCP server works with the same URL. Add the server the way you add other remote MCP servers in that client.
Authorizing access
When you authorize your agent for the first time: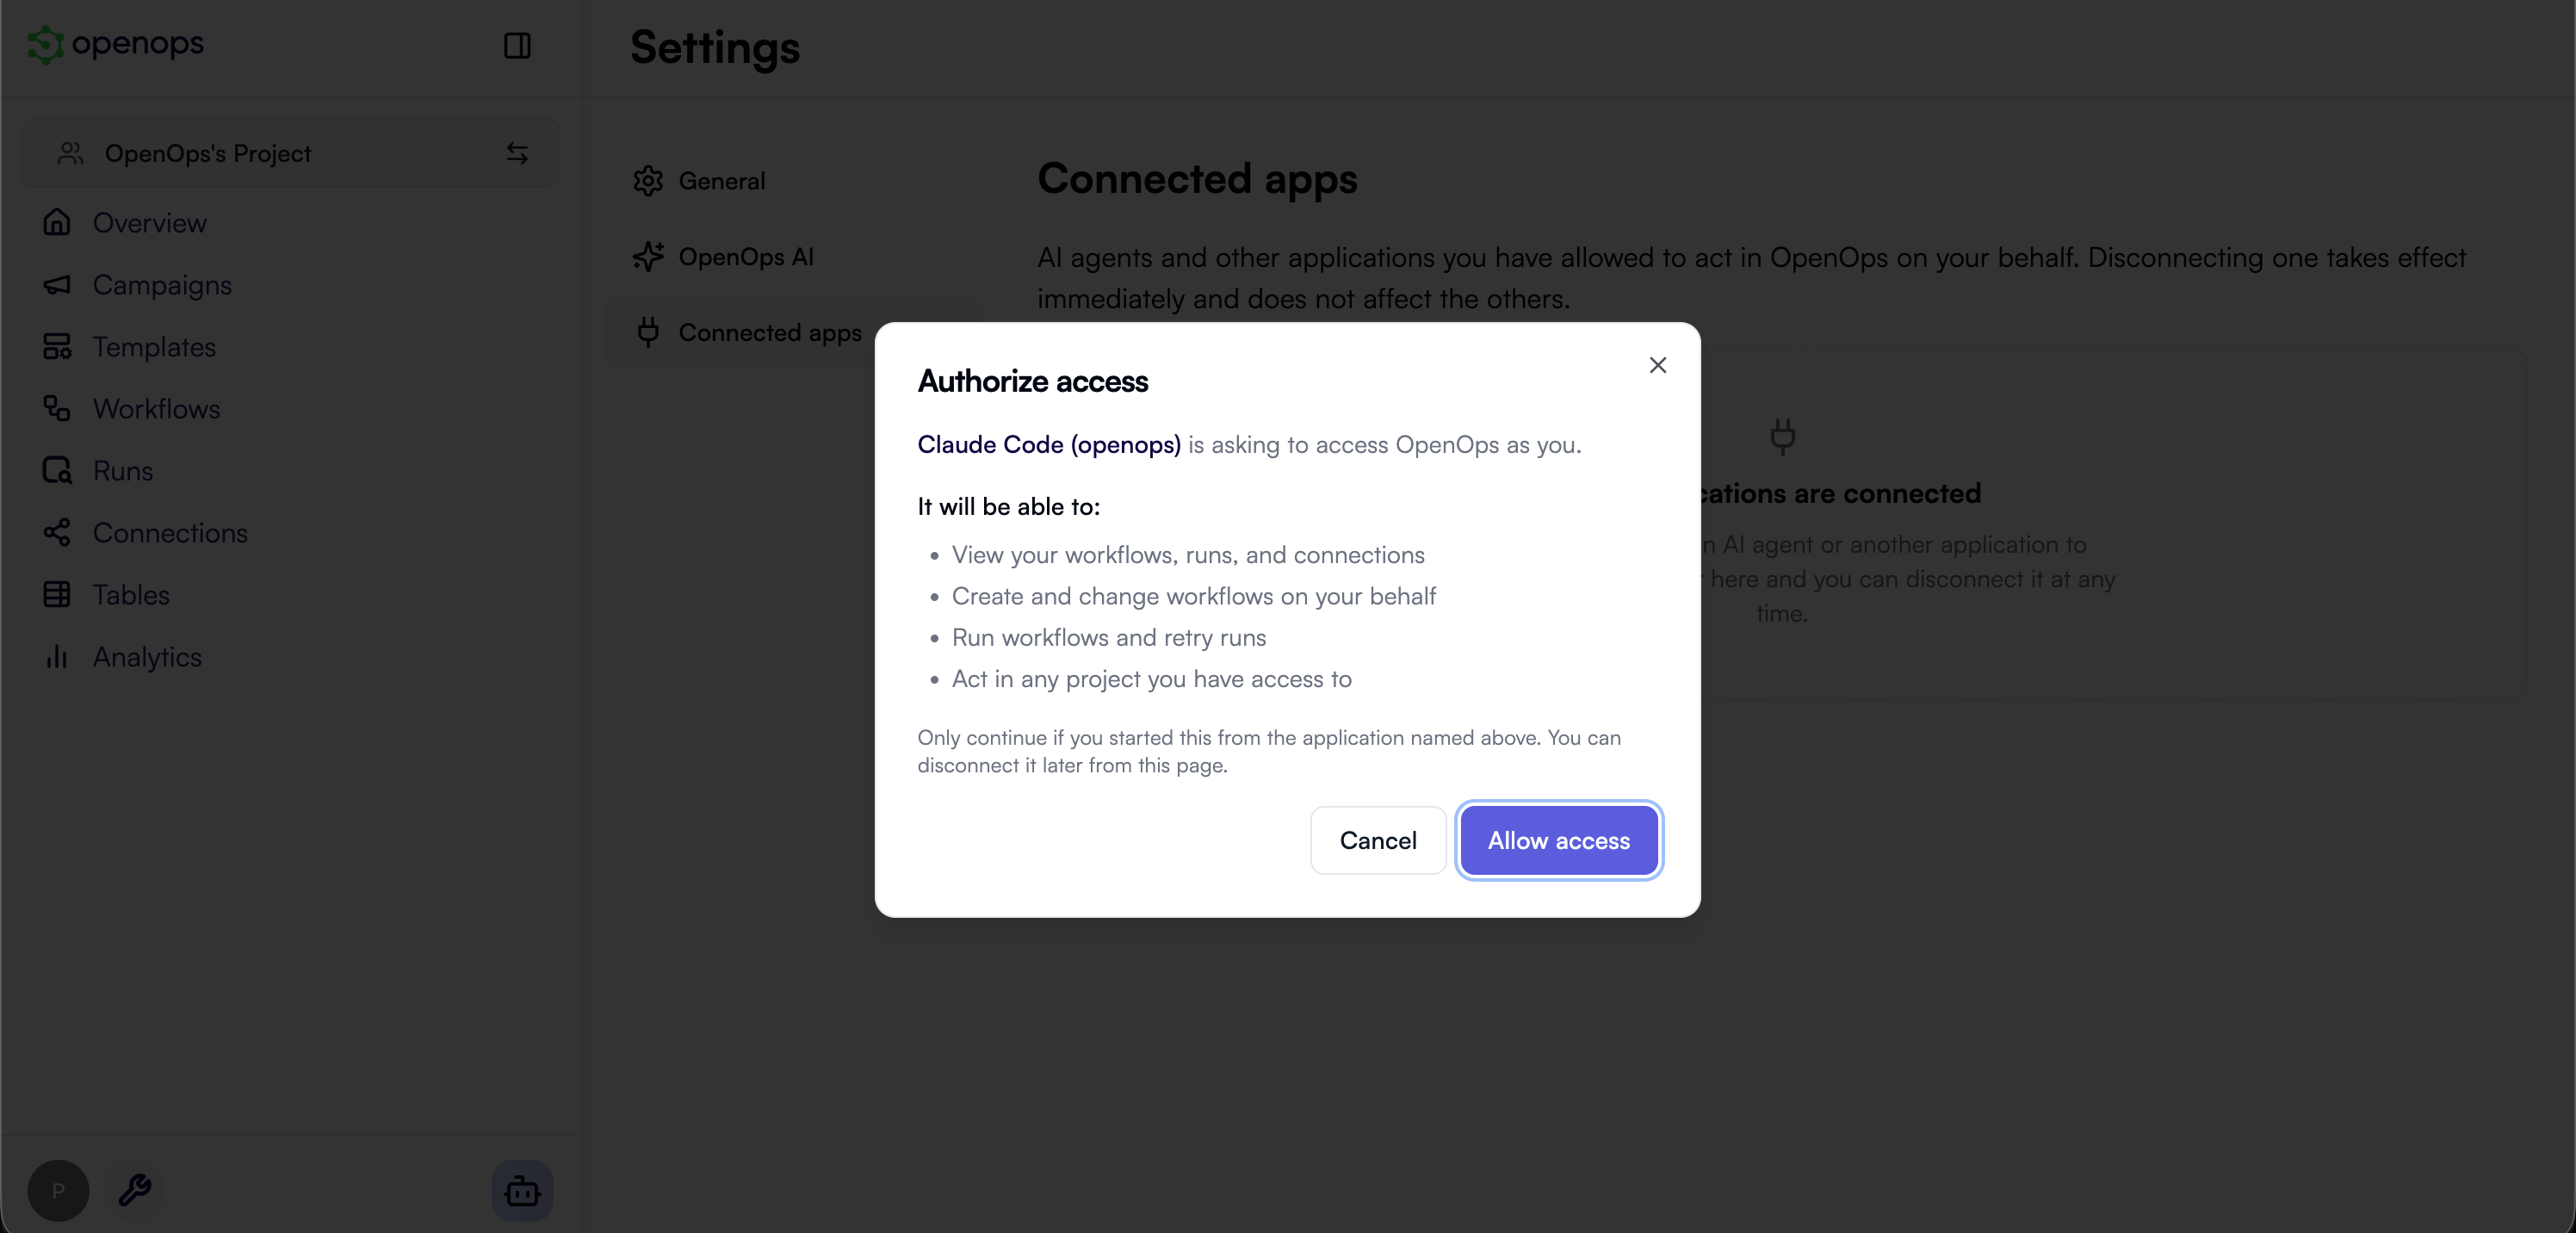
- When you start authorization from your agent, it opens OpenOps in your browser. If you’re not logged in, log in first.
- OpenOps shows the Authorize access dialog on the Connected apps settings page. The dialog names the application asking for access and lists what it will be able to do:
- View your workflows, runs, and connections
- Create and change workflows on your behalf
- Run workflows and retry runs
- Act in any project you have access to
- Click Allow access. The browser returns control to the agent, which now has access to the OpenOps tools. To deny the request, click Cancel or close the dialog.
Only approve requests you started: The dialog shows the name of the application asking for access. If you didn’t start connecting from that application, click Cancel.
Using your agent with OpenOps
Once connected, ask your agent about your OpenOps environment in plain language. For example:- “Which workflows are enabled in my OpenOps environment, and what do they do?”
- “Show me the failed runs of the EBS gp2 to gp3 migration workflow from this week and explain why they failed.”
- “Retry the run that failed this morning.”
- “Which connections does the Slack notification workflow use?”
- “Create a workflow that finds unattached Elastic IPs every Monday and posts them to Slack, then test the first step.” (Enterprise edition)
- “Switch to the Production workspace and list its workflows.” (Enterprise edition)
What the agent can do
The tools available to the agent depend on your OpenOps edition. See pricing for the differences between editions.Workspaces (Enterprise edition): An authorized agent isn’t limited to one workspace. Name the workspace you want to work in, and the agent passes it along with each request. If you don’t name one, the agent acts in your default workspace.
Managing connected apps
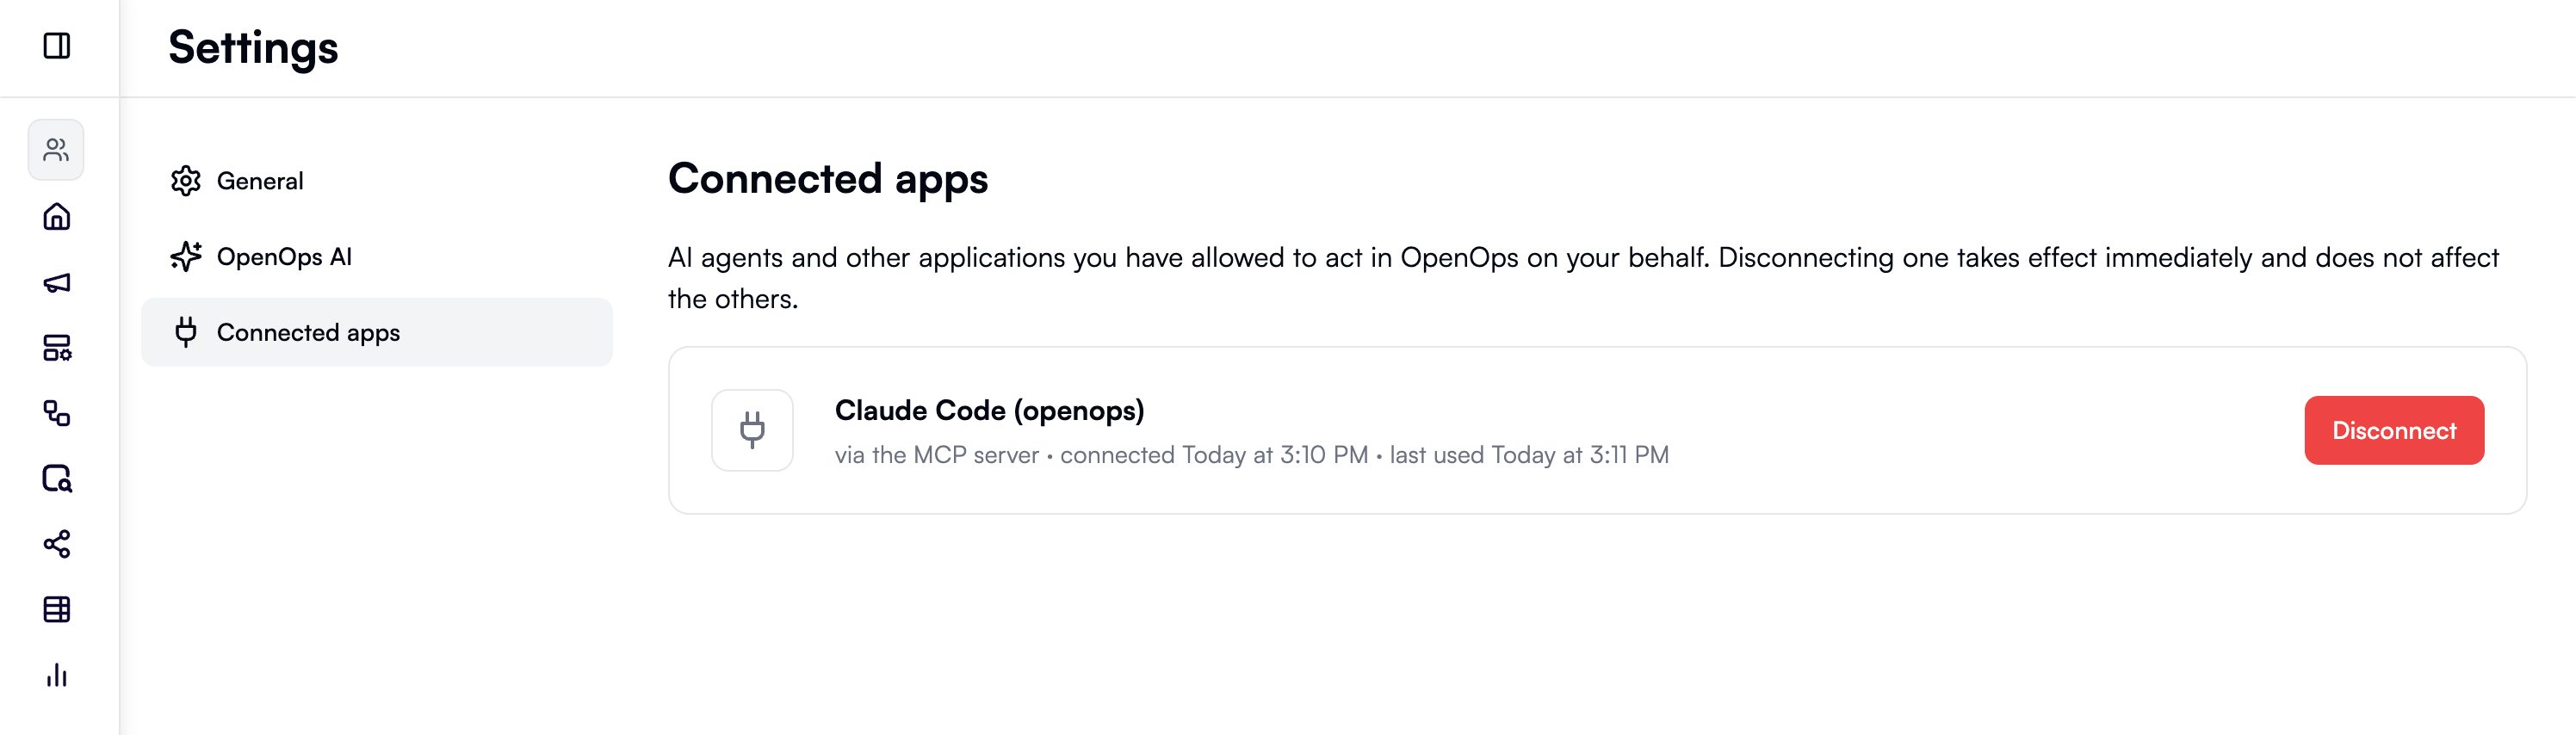
- In the OpenOps left sidebar, click the Settings icon at the bottom.
- In the Settings view, click Connected apps. Each entry shows the application name, when it was connected, and when it was last used. If you connect the same agent from two machines, you see two entries.
- To revoke access, click Disconnect next to an entry and confirm. The agent loses access immediately and has to be authorized again to reconnect. Other connected apps aren’t affected.
Enabling the MCP server
This section is for OpenOps administrators. The MCP server is disabled by default and requires OpenOps 0.7.0 or later. To upgrade, see Updating OpenOps. Agents sign in through OAuth, which OpenOps serves only over HTTPS; plainhttp is accepted only when OPS_PUBLIC_URL is http://localhost.
Docker Compose
- Enable TLS for your installation. See Enabling TLS in the deployment guide.
- Open the
.envfile in your OpenOps installation directory and set the following variables. If your installation was created before 0.7.0, the variables aren’t in the file yet, so add them:Generate the secret withopenssl rand -hex 32. The MCP container doesn’t start while the secret is empty.COMPOSE_PROFILES=mcpmakesdocker compose up -dstart the MCP container. - After making any changes to the
.envfile, restart the OpenOps containers: - Verify that the server is reachable:
The command returns a JSON document that names your host as the
resource. A502 Bad Gatewayresponse means the MCP container isn’t running. Check thatCOMPOSE_PROFILES=mcpis set and the secret isn’t empty, then inspect the container withsudo docker compose logs openops-mcp.
OPS_OAUTH_ENABLED=false, remove the COMPOSE_PROFILES=mcp line, and run sudo docker compose --profile mcp down followed by sudo docker compose up -d. All connected agents lose access.
Helm chart
The OpenOps Helm chart version 0.7.0 or later includes the MCP server as an opt-in component. Your release must already serve OpenOps over HTTPS, whether through the chart’s ingress TLS settings or a load balancer that terminates TLS. See TLS/HTTPS configuration in the chart’s README. Then add the following to your values file and upgrade the release:publicUrl. See MCP server for external agents in the chart’s README for details, including how to supply the secret from an external secret manager.
Troubleshooting
- The agent reports that the server needs authentication: Run the agent’s login step, such as
/mcpin Claude Code orcodex mcp login openops, and check that the server URL ends with/mcp. - The browser shows “This authorization request cannot be completed”: The request has expired or has already been used. Connect again from your agent.
- Tool calls fail with an authorization error after working before: The agent was disconnected in Connected apps, your user account was deactivated, or the agent hasn’t been used for 30 days. Connect again from your agent.
- The agent works in the wrong workspace (Enterprise edition): Name the workspace in your prompt. See the note in What the agent can do.